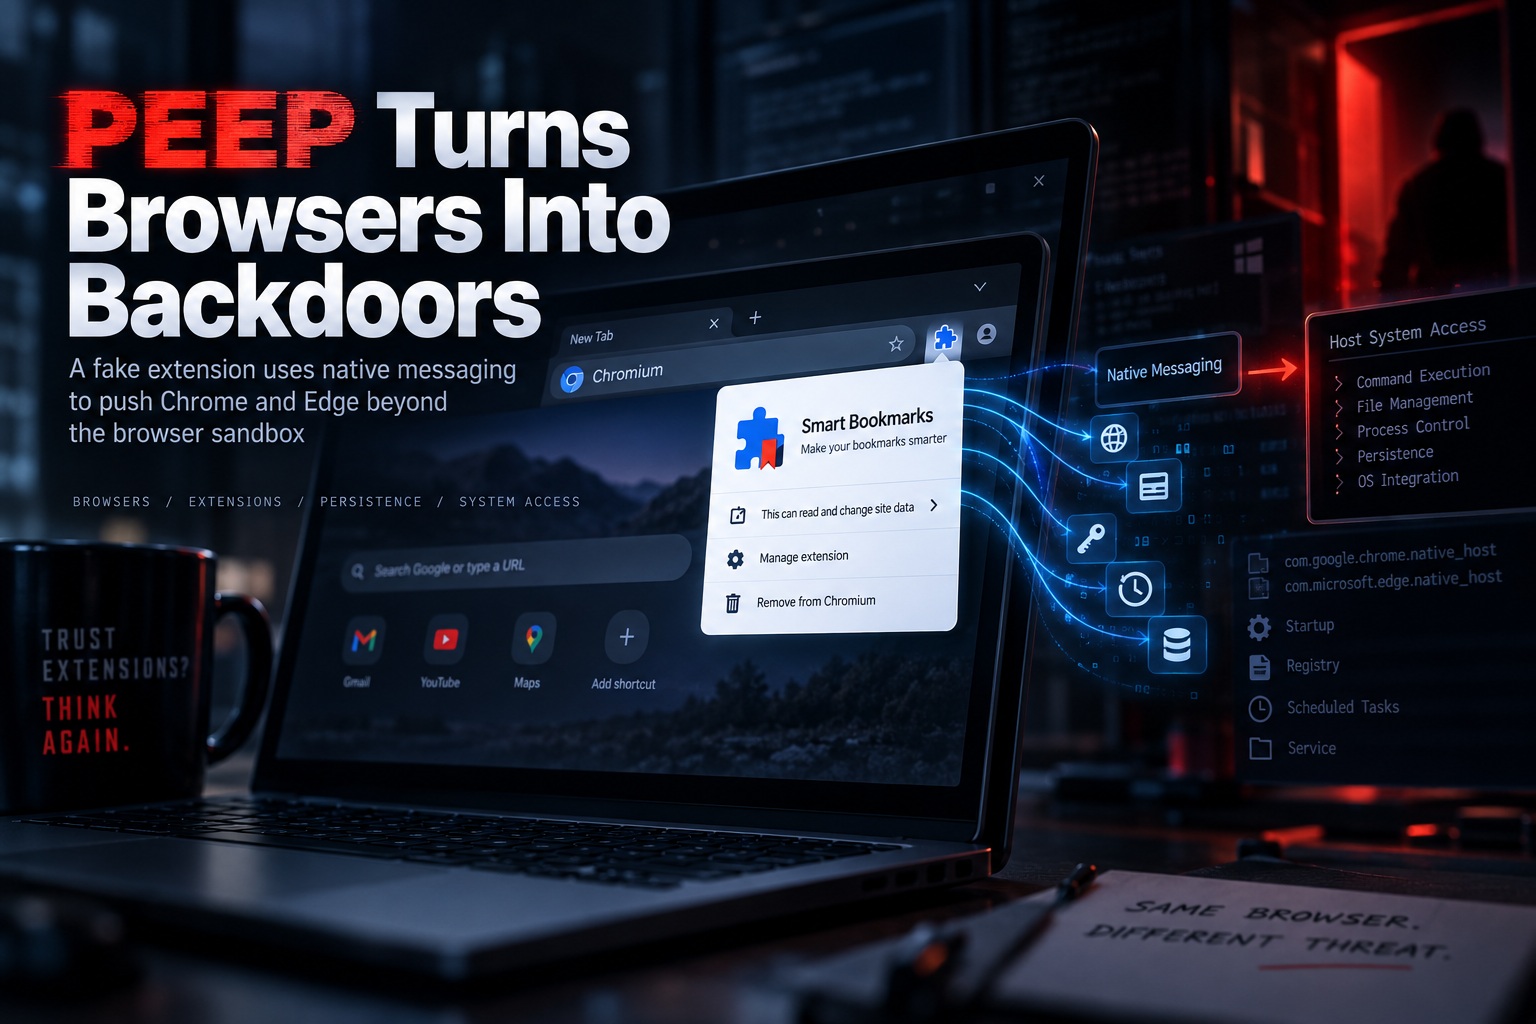
PEEP is described as a post-compromise framework as it lacks an initial access vector itself, meaning it requires the operator to breach a machine through some other means and deploy the malware. The activity remains unattributed, although the presence of Chinese-language artifacts in the source code points to a Chinese-speaking threat actor.
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution